Resilient by default, across every framework you answer to.
Digital resilience by default, run for you
Making companiesdigitally resilientby default
We own and run it for you with one control tower that unifies your governance policies, security practices and compliance proofs.
- Governance policies
- Security practices
- Compliance proofs
Agents collect, the platform proves, experts decide
Always on, so nobody chases screenshots
Agents read your systems, collect the evidence and find the gaps. They run all the time, not just in the weeks before an audit.
Autonomous Agents →The control tower where it all runs
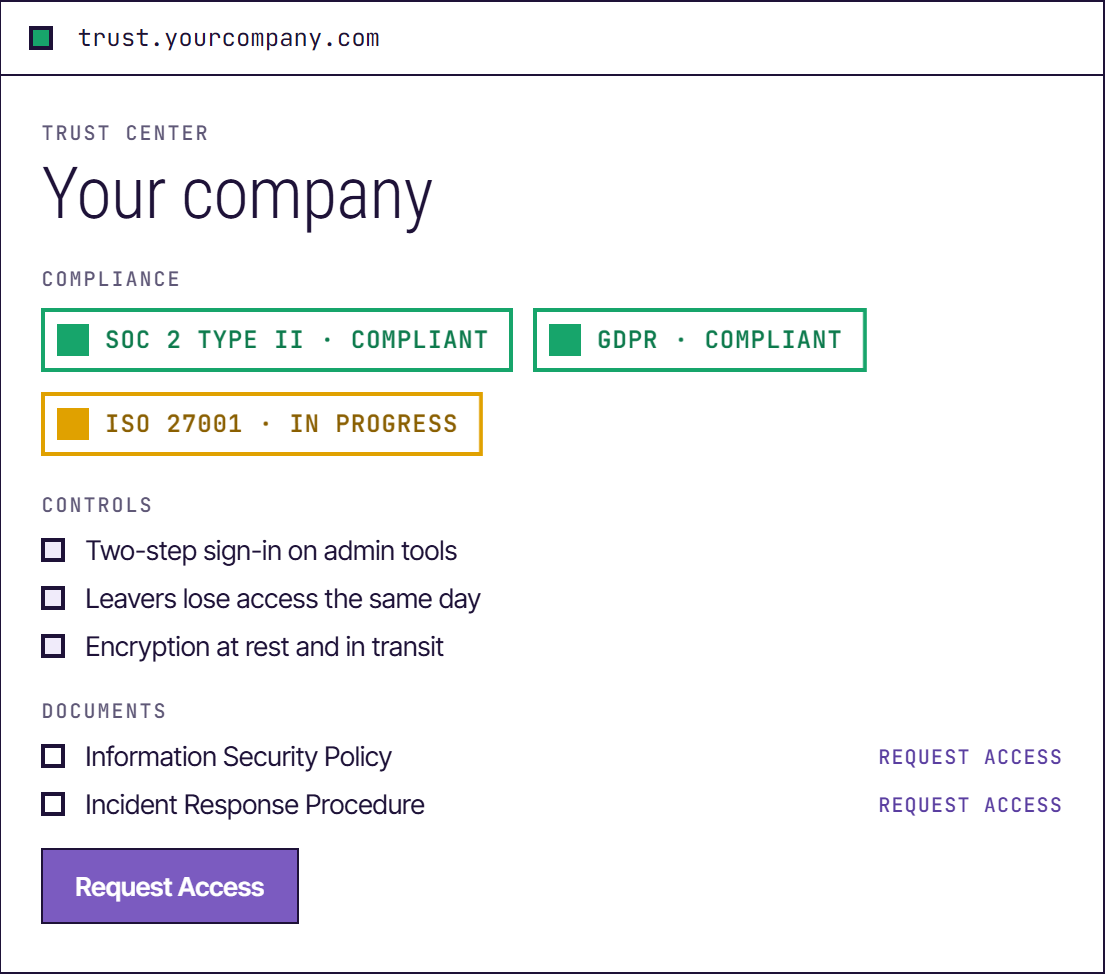
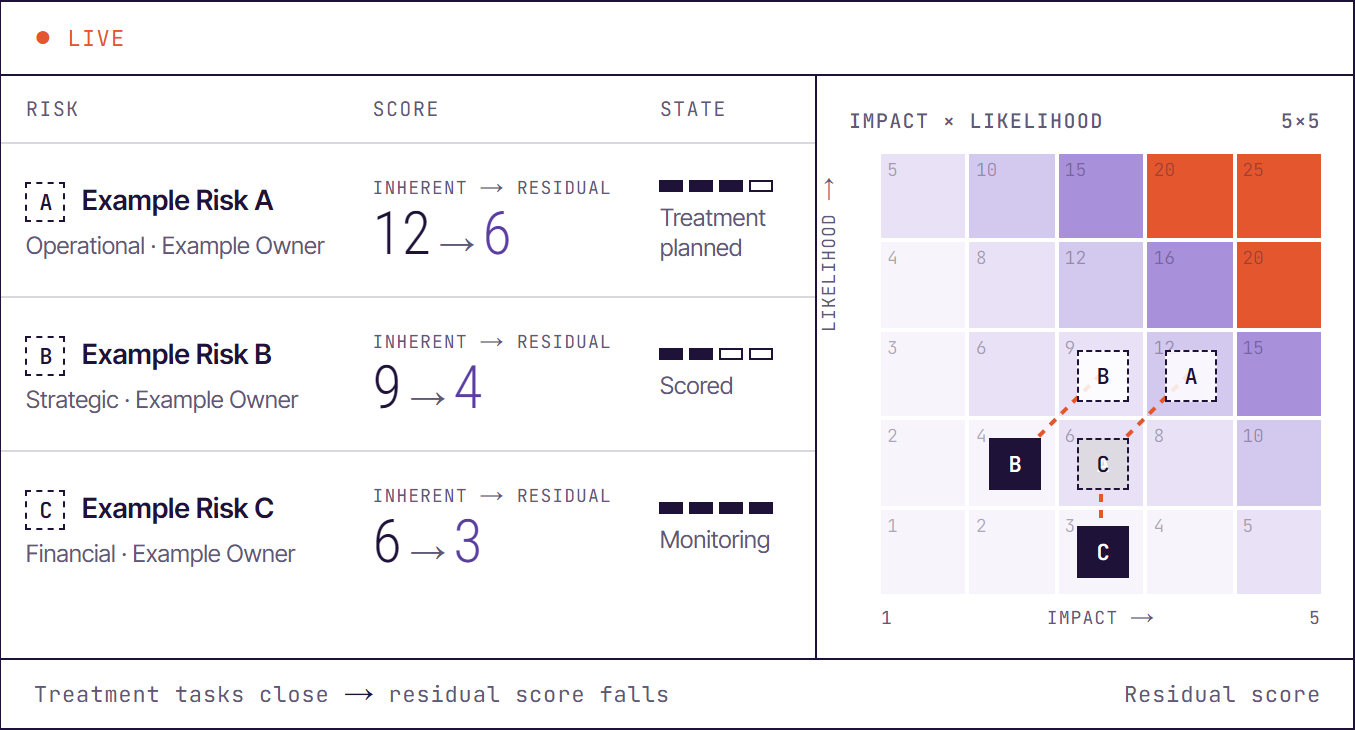
Governance policies, security practices and compliance proofs in one place. We set a resilience stage for your growth, then keep proving it with continuous attestations.
Audit Management →Judgement stays human
Experts work inside your team. They tell you what to fix, how and when, and help you decide where nuance matters, so the advice fits your company.
GRC Experts →
How it grows with you
Built for every stage of trust
The same three parts work together at every stage of your company. As you grow, they take you up one level at a time. Each level adds controls, and nothing restarts.
- Autonomous agents check and collect, all the time
- Platform holds the controls and the proof
- Forward deployed experts make the calls and close the gaps
Proof that holds up in enterprise procurement.
Answer the security questions without building a compliance team first.
The problem
Policies and practice tell two different stories
Today, company policies and everyday practices tell two different stories, leaving security gaps unnoticed. These gaps can cause huge financial losses and reputational damage, and even threaten a company's survival.
- Everyone signs in with two-step verificationSome accounts never turned it on
- Laptops are encryptedA few older ones are not
- Access is reviewed every quarterThe last review was over a year ago
Illustrative example
- Huge financial losses
- Reputational damage
- A threat to survival
Today's alternatives
The usual routes cost a lot, and still leave the work with you
To solve this, companies spend two to three lakh rupees on a consulting engagement, or over twenty-five lakh rupees a year hiring a full-time CISO. Yet their engineering teams still have to spend around six hundred hours setting up security practices.
| What you need | A compliance tool | A consultant | A hire | packets |
|---|---|---|---|---|
| Who is accountable | Gap: Your engineer | Gap: Nobody, after engagement ends | Partly: Whoever you hired, once ramped | Covered: Named Compliance Lead, week one |
| Who does the work | Gap: You | Partly: Advises; you implement | Partly: One person, part-time | Covered: Agents at volume + specialists |
| Policies and evidence | Partly: Templates to fill in | Partly: Document set, handed over | Gap: Written from scratch | Covered: Drafted & mapped; you approve |
| Continuous monitoring | Covered: Yes | Gap: No system | Partly: Manual, or a tool too | Covered: Yes, same system |
| Adding a framework | Gap: Start the checklist again | Gap: A new engagement | Partly: More work, same person | Covered: Reuses controls in place |
| Year two | Partly: Renews; work still yours | Gap: Starts from scratch | Gap: Depends on them staying | Covered: Continuous, nothing restarts |
| What it costs | Partly: Licence, plus the work | Partly: Project fee, no system | Gap: ₹30–35L/year, plus 2–3 months to hire | Covered: One fixed price |
What it covers
Modules that plug into the platform
Each module runs on the same control tower. Agents do the work that can be automated, and an expert owns the judgement.

Use AI fast, with every use case governed
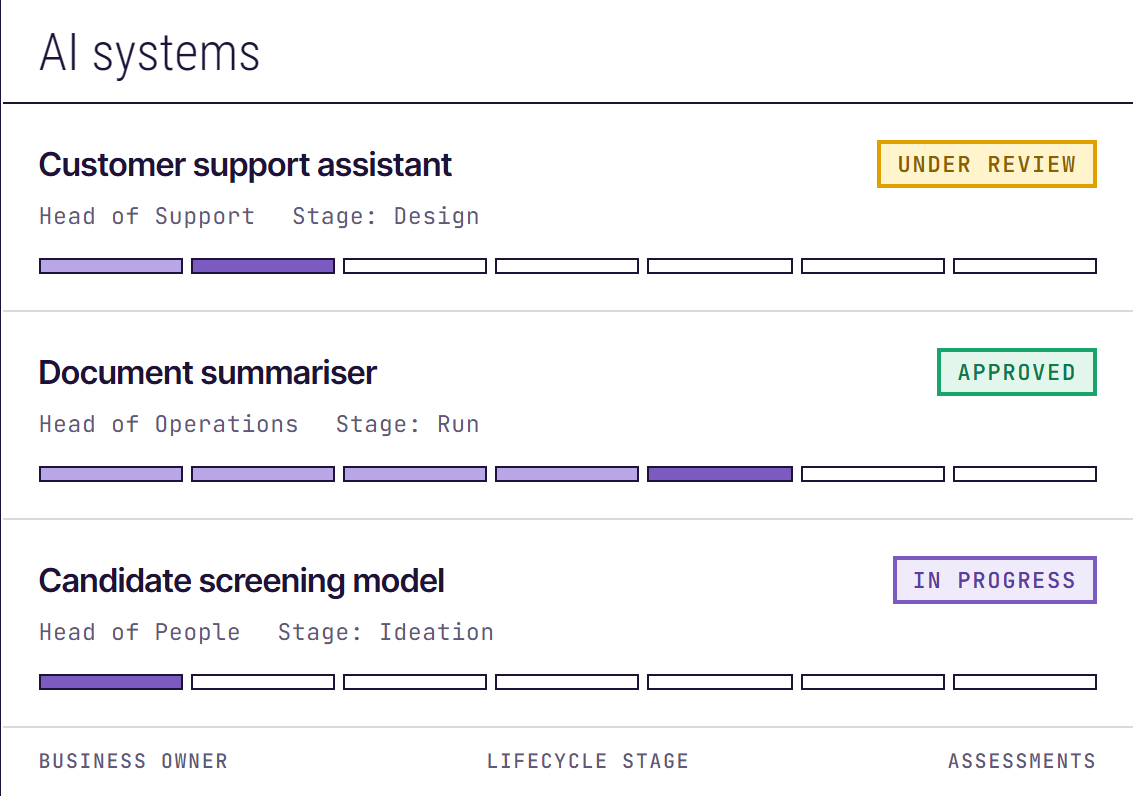
Register AI systems, assess them as they move through their lifecycle, and keep controls, tasks and evidence with each one. Named approval groups review what needs review.
Learn more →Stop losing monthsto a questionnaire.
Get your audit score in two minutes, or talk to us about the program. Either way you’ll know where you stand before you spend anything.